Passwordless sign-in
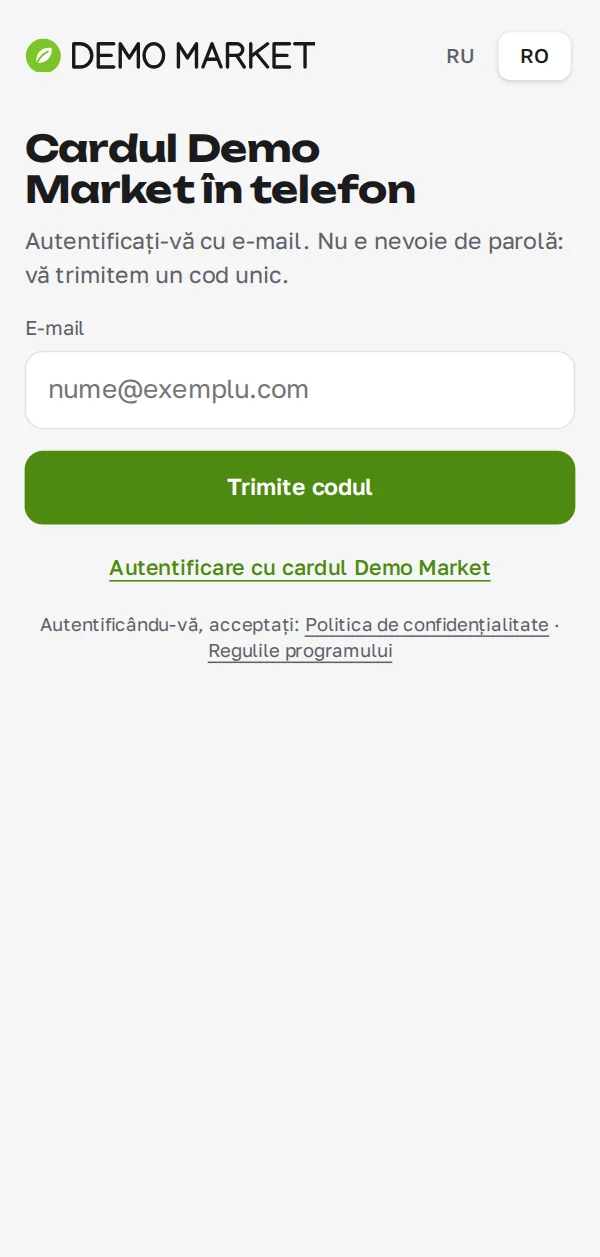
A one-time 6-digit code by e-mail, valid for 10 minutes, with a limited number of attempts. The response is the same for existing and non-existing addresses.
How customer data is protected, what rights the customer has in the app and how Synngate Loyalty takes into account Moldova's personal data protection law.
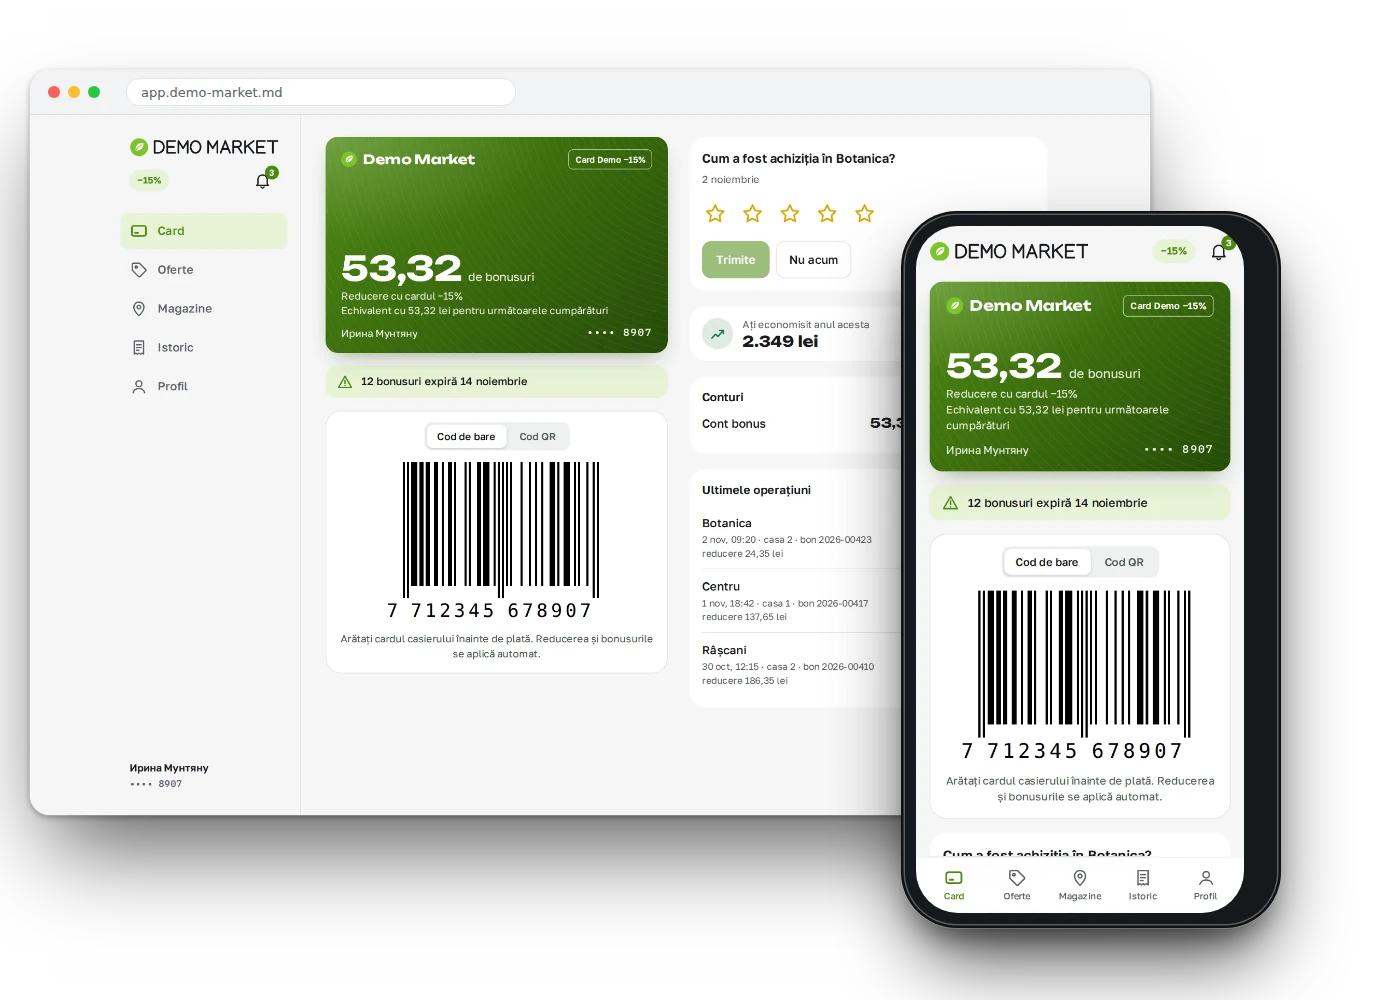
Customer data security is built into the solution from day one, not added later. Law No. 195/2024 on personal data protection (Moldova) defines the shopper's rights, and Synngate Loyalty takes into account the requirements of Legea nr. 195/2024: consents, data export and deletion. The store's lawyer agrees the policy texts and program rules.
A one-time 6-digit code by e-mail, valid for 10 minutes, with a limited number of attempts. The response is the same for existing and non-existing addresses.
The session is not accessible to page scripts and travels only over HTTPS. The database stores only a fingerprint of the token, and requests are protected against forgery.
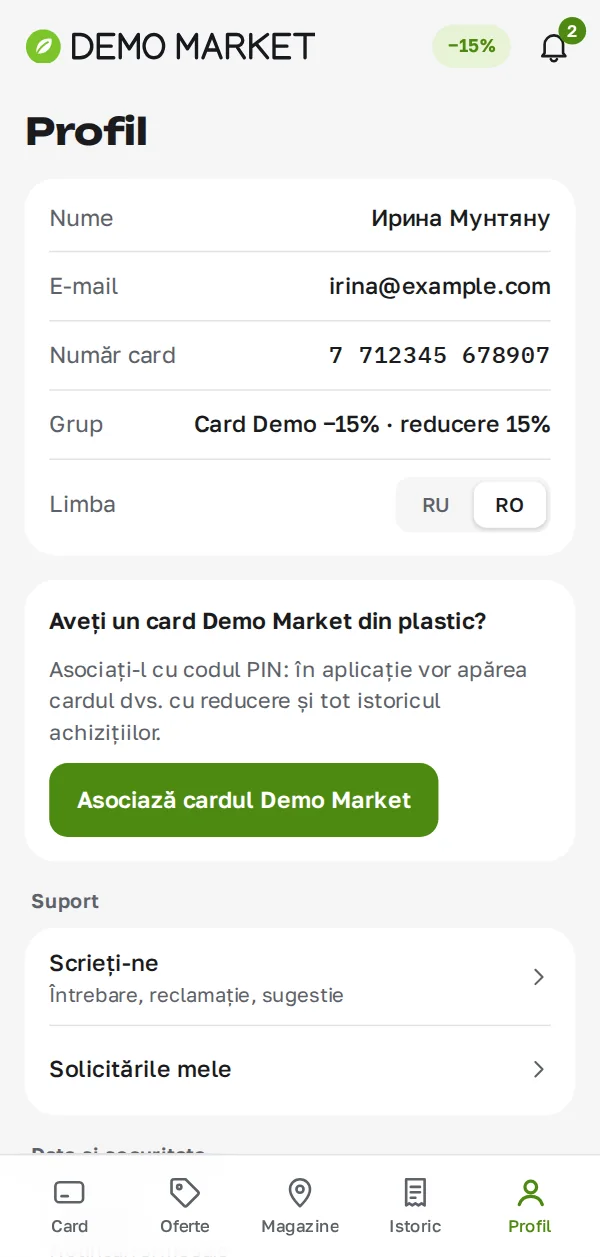
A customer sees only their own card, receipts and bonuses. This is enforced on the server, not in the interface.
Attempt limits per card, account, address and across the system make a PIN impossible to guess.
The app does not call third-party sites: fonts, images and code are our own.
Uploaded images are re-encoded, and camera data and geotags are removed.
The marketer cabinet is reachable only from the internal network, with sign-in by a platform account.
Sign-in events and cabinet actions are written to a log.
Mailings go only to those who gave consent.
Protection is verified by hundreds of automated checks, including attack scenarios: guessing codes and PINs, attempts to see another person's data.
Rights are granted by role and action: who can view customers, who can change rules.
The till API is bound to the point of sale: one store's key does not work in another.
Incoming API requests and exchanges with external systems are recorded, so a disputed receipt can be traced.
We do not replace legal advice. Check the policy, consents and retention period with a lawyer.
The solution takes into account the requirements of Legea nr. 195/2024: consents, data export and deletion. A legal assessment for your company is given by a lawyer.
No. Sign-in uses a one-time e-mail code, so there is nothing to forget or steal.
Staff with rights in the center and the cabinet. Their actions are logged.
A 30-minute conversation about your loyalty program, with no generic slides.